Cyber Resilience Act Readiness for Mobile Machinery

What OEMs Should Know About the Cyber Resilience Act and EU Machinery Regulation

New European Union cybersecurity requirements will affect mobile machinery and off-highway equipment that incorporates connected products, embedded software, electronic controls, displays, telematics, and other digital elements.

The Cyber Resilience Act, EU Machinery Regulation, and related requirements will introduce new responsibilities for manufacturers that sell equipment in the European market. These requirements extend beyond initial product design. They address how cybersecurity is documented, monitored, maintained, and supported throughout the product lifecycle.

Talk With Kraft About CRA Readiness

What is Changing?

Manufacturers will be expected to demonstrate that cybersecurity has been considered throughout the design, production, operation, maintenance, and support of products with digital elements.

Depending on the product and application, this may include:

  • Identifying and documenting cybersecurity risks
  • Maintaining a software bill of materials, or SBOM
  • Controlling access to software and electronic systems
  • Implementing appropriate technical security controls, which may include secure boot and signed firmware
  • Providing secure software and firmware updates
  • Monitoring for vulnerabilities after a product enters the market
  • Reporting actively exploited vulnerabilities and serious security incidents
  • Supporting security updates for the required product support period

These responsibilities may affect both complete machine manufacturers and the suppliers providing the electronic components, software, and connected systems used within the machine.

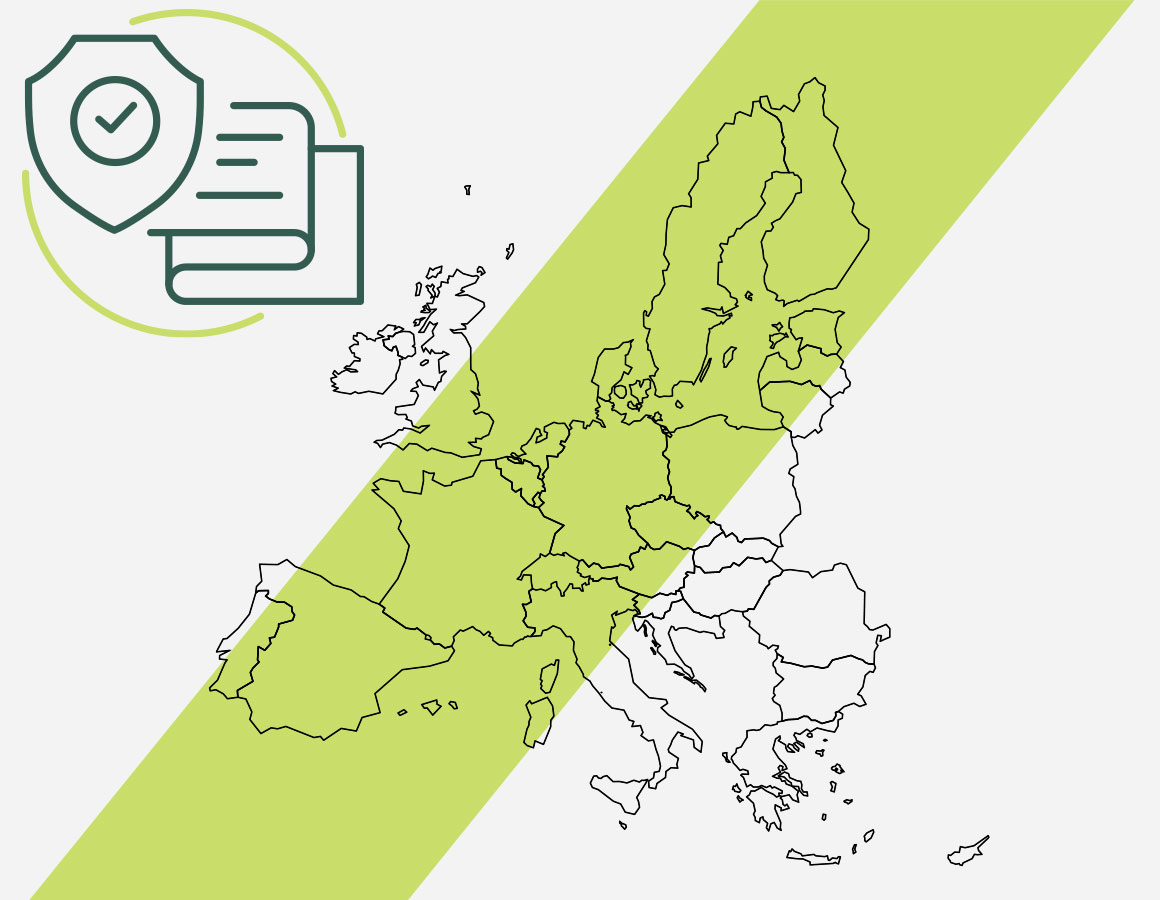
Key Dates and Timeline

The CRA is part of a broader set of EU regulations that are converging around cybersecurity and machine safety.

Key milestones include:

September 2026

CRA vulnerability reporting obligations begin

Janurary 20, 2027

EU Machinery Regulation applies

December 2027

Most CRA requirements become fully applicable

Who Does this Apply to?

The CRA and related regulations apply to:

  • OEMs that place machines on the EU market
  • Manufacturers of mobile and off-highway equipment with digital or connected components
  • Products with digital elements that connect directly or indirectly to other devices or networks

Talk With Kraft About CRA Readiness

What OEMs Should be Prepared for

The CRA introduces several new expectations that directly affect machine design and long-term support.

application icon

Software Bill of Materials (SBOMs)

OEMs must be able to identify and document the software components used in their products. This enables vulnerability tracking and response over time.

icon of software design

Vulnerability Management

Manufacturers are expected to monitor for vulnerabilities, apply mitigations or updates, and report actively exploited vulnerabilities starting in 2026.

icon of choosing components

Secure Updates

Products must support secure firmware and software updates to address vulnerabilities during their operational life.

icon of support

Lifecycle Security

Cybersecurity must be addressed across the full product lifecycle, including support periods, update availability, and defined end-of-life processes. This is especially important for machinery that remains in service for many years.

electric drives team

Kraft’s Role

Kraft Mobile Systems is preparing to support OEMs through this transition as a system integrator and partner.

Our focus includes:

  • Translating regulatory requirements into practical system-level decisions
  • Aligning with key suppliers that are investing heavily in secure-by-design platforms
  • Minimizing redesign impact through thoughtful system architecture
  • Supporting secure boot, signed firmware, secure communication, and update strategies
  • Helping OEMs plan documentation, lifecycle support, and long-term compliance

Talk With Kraft About CRA Readiness

If you would like to discuss how the CRA may impact your machines, fill out the form below and we’ll be in touch.

Cyber Security Page Subscribe

This field is for validation purposes and should be left unchanged.